THE PLATFORM
Your compliance program, pre-structured and ready to run.
domainGRC replaces the “spreadsheets and shared drives” approach with a connected compliance system, loaded with your framework controls, your compliance calendar, and the expert practitioner-built policies your auditor expects to see.
How the platform is organized.
domainGRC is organized around three areas that mirror how a real compliance program operates: managing your ongoing compliance activities, tracking the assets your program covers, and running your audit when the time comes. Everything connects.
myDomain: Run your compliance program
The operational core of your compliance program. This is where your recurring activities live, your IT service desk runs, your risks are tracked, and your corrective actions are managed.
- Pre-loaded with framework controls
- Compliance calendar on day one to help you hit the ground running
- Evidence flows to every control it supports - no repeat uploads
assetMGR: Know what you’re protecting
A structured inventory of all organizational assets.
- Link any asset to the controls and risks that govern it
- Understand related assets that shape the risk profile
- Audit trails of employee lifecycle events, access requests, hardware provisioned, and maintenance performed.
myAudit: Where you and your assessor work together
Upload your assessor’s Information Request List to domainGRC and invite them directly into your domain with scoped, time-limited access.
- Assessors review and approve evidence or request additional info live
- Artifact owners notified automatically when items need rework
- Track audit status through theDash in real-time
Interconnected web
Every record can be linked to every other - people, software, hardware, information, and facilities are stored as an interconnected web.
- Understands the ripple effects when anything changes
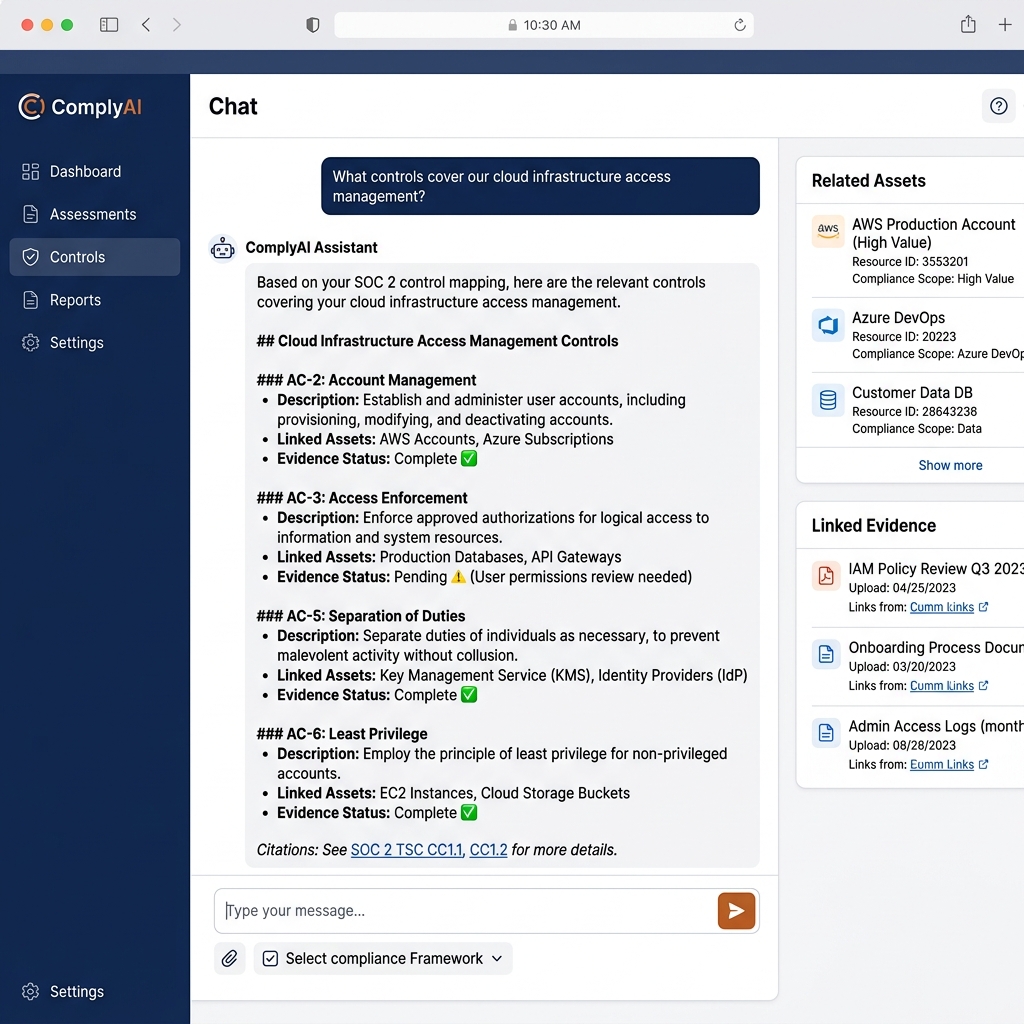
AI compliance assistant (private beta)
A conversational AI assistant is built into domainGRC to help you get answers faster. Ask questions about your program, generate compliance documents like a Business Impact Analysis, or explore how risks and controls connect across your environment - all in a natural language.
- In private beta now, with a broader rollout planned for H2 2026
Audit trail with field-level change history
Every change to every control, asset, and artifact record is timestamped and attributed to a specific user.
- Always know who changed what, and when it happened
Evidence library with versioning
Centralized evidence and controls that travel across audit periods as things change.
- Historical context from your last audit is archived but remains available for reference
Assessor collaboration in-platform
Give assessors scoped, time-limited access to review evidence live and work through your Information Request List directly in the platform.
- Assessors flag items needing rework, notifying artifact owners automatically
Multi-framework support, no upcharge
All your frameworks in one place. The platform grows with you as you need new frameworks or expand scope.
- No upcharges for adding additional frameworks
This year's work becomes next year's blueprint.
domainGRC replaces spreadsheets with a structured rollover system. After each audit, the platform retains:
- Tested controls and collected evidence
- Cited policies and assessed risks
- Owners who closed each task
Next year’s cycle starts from last year’s blueprint. Recurring controls roll over with one click. Anything that changed since the last cycle (new assets, new vendors, new policies, departed owners, expanded scope) is flagged for review. Each cycle becomes more efficient than the last, because you are refreshing a working record instead of rebuilding a spreadsheet.
AI-NATIVE COMPLIANCE PLATFORM
Built for AI from the data up.
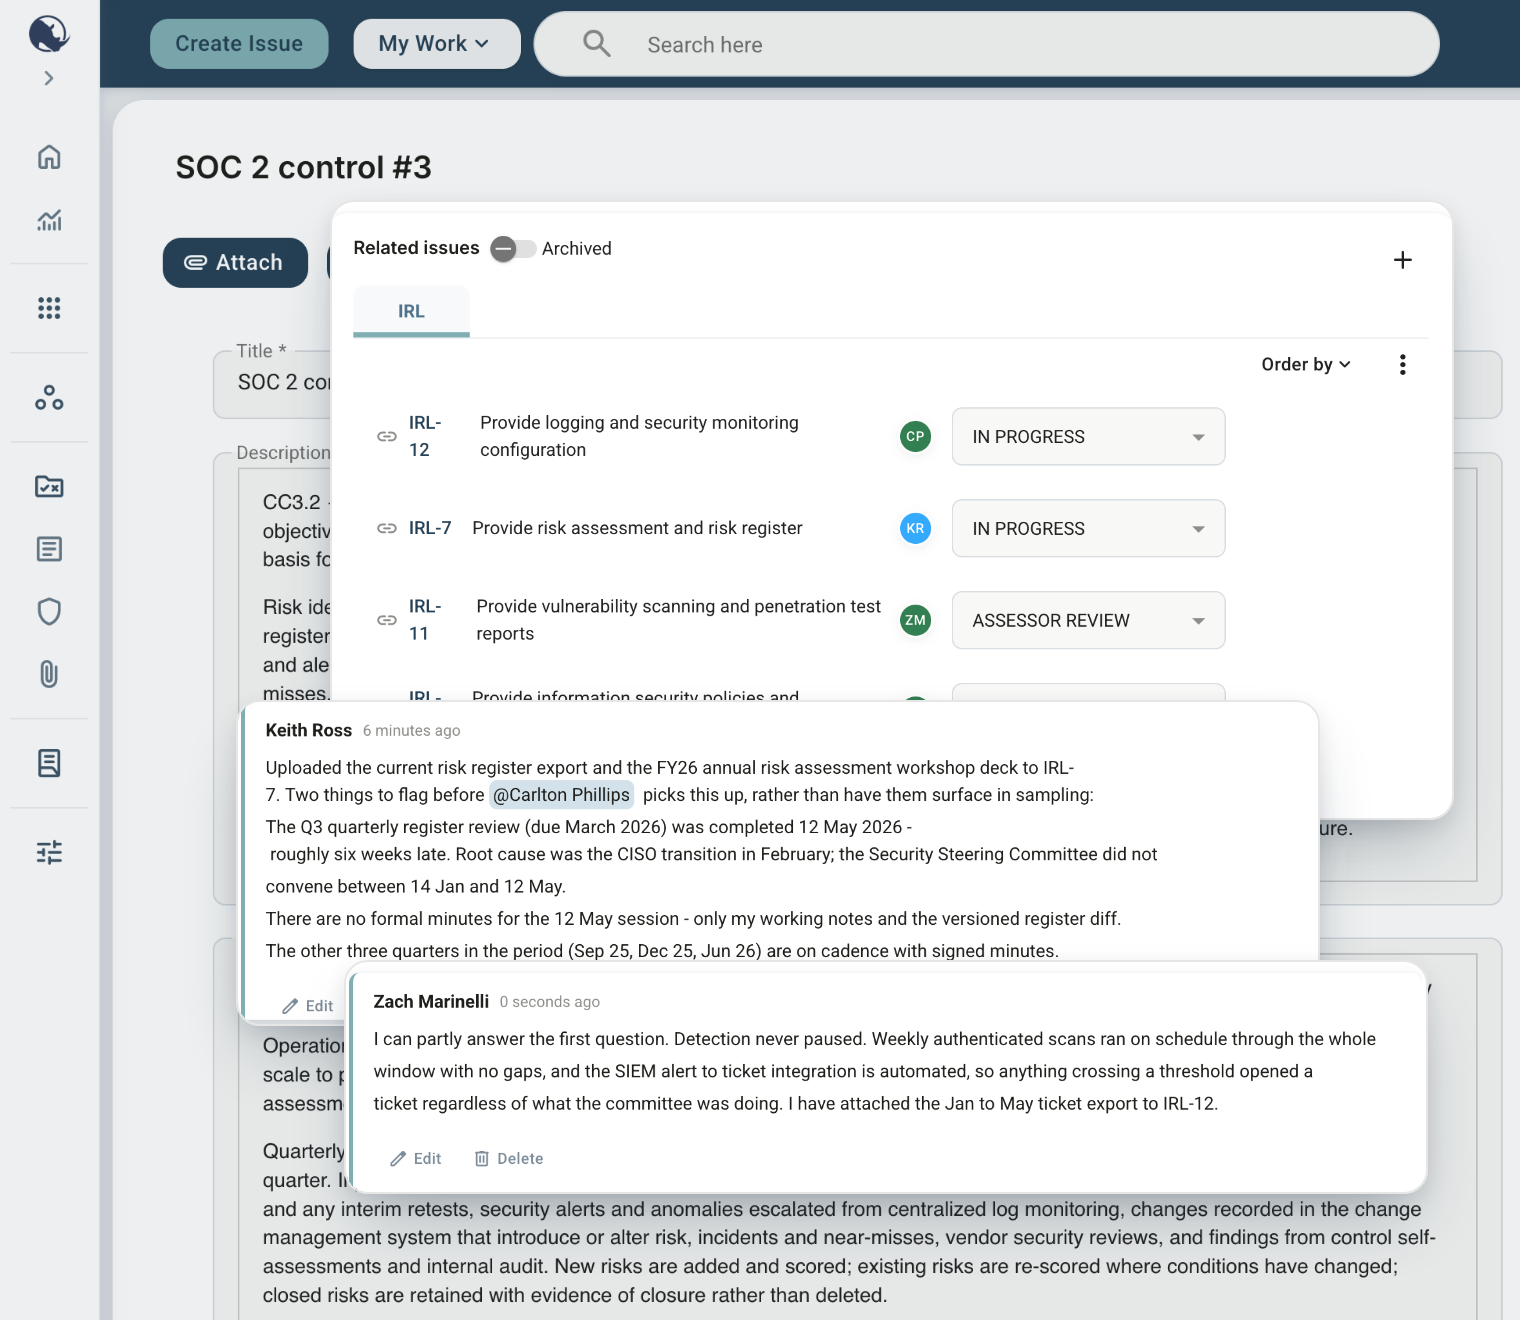
Our AI compliance assistant works inside your program. Each session is bound to a single organization, and that scope is enforced server-side. Before it answers, the assistant queries your data.
- Searches your issues, audits, and attachments, including the text inside uploaded PDFs and SOPs
- Answers policy and standards questions only from documents in your knowledge base, and cites the document and source file behind every answer
- Reads the exact figures from your live program data to answer questions and build charts, rather than estimating them
- Creates and updates records, from issues to audits to relationships, after echoing the plan back to you for confirmation
The refusals matter as much as the answers. Ask a compliance question your knowledge base cannot support and the assistant tells you so and asks you to upload the policy, rather than answering from a model's general training. In private beta now, with a broader rollout planned for H2 2026.
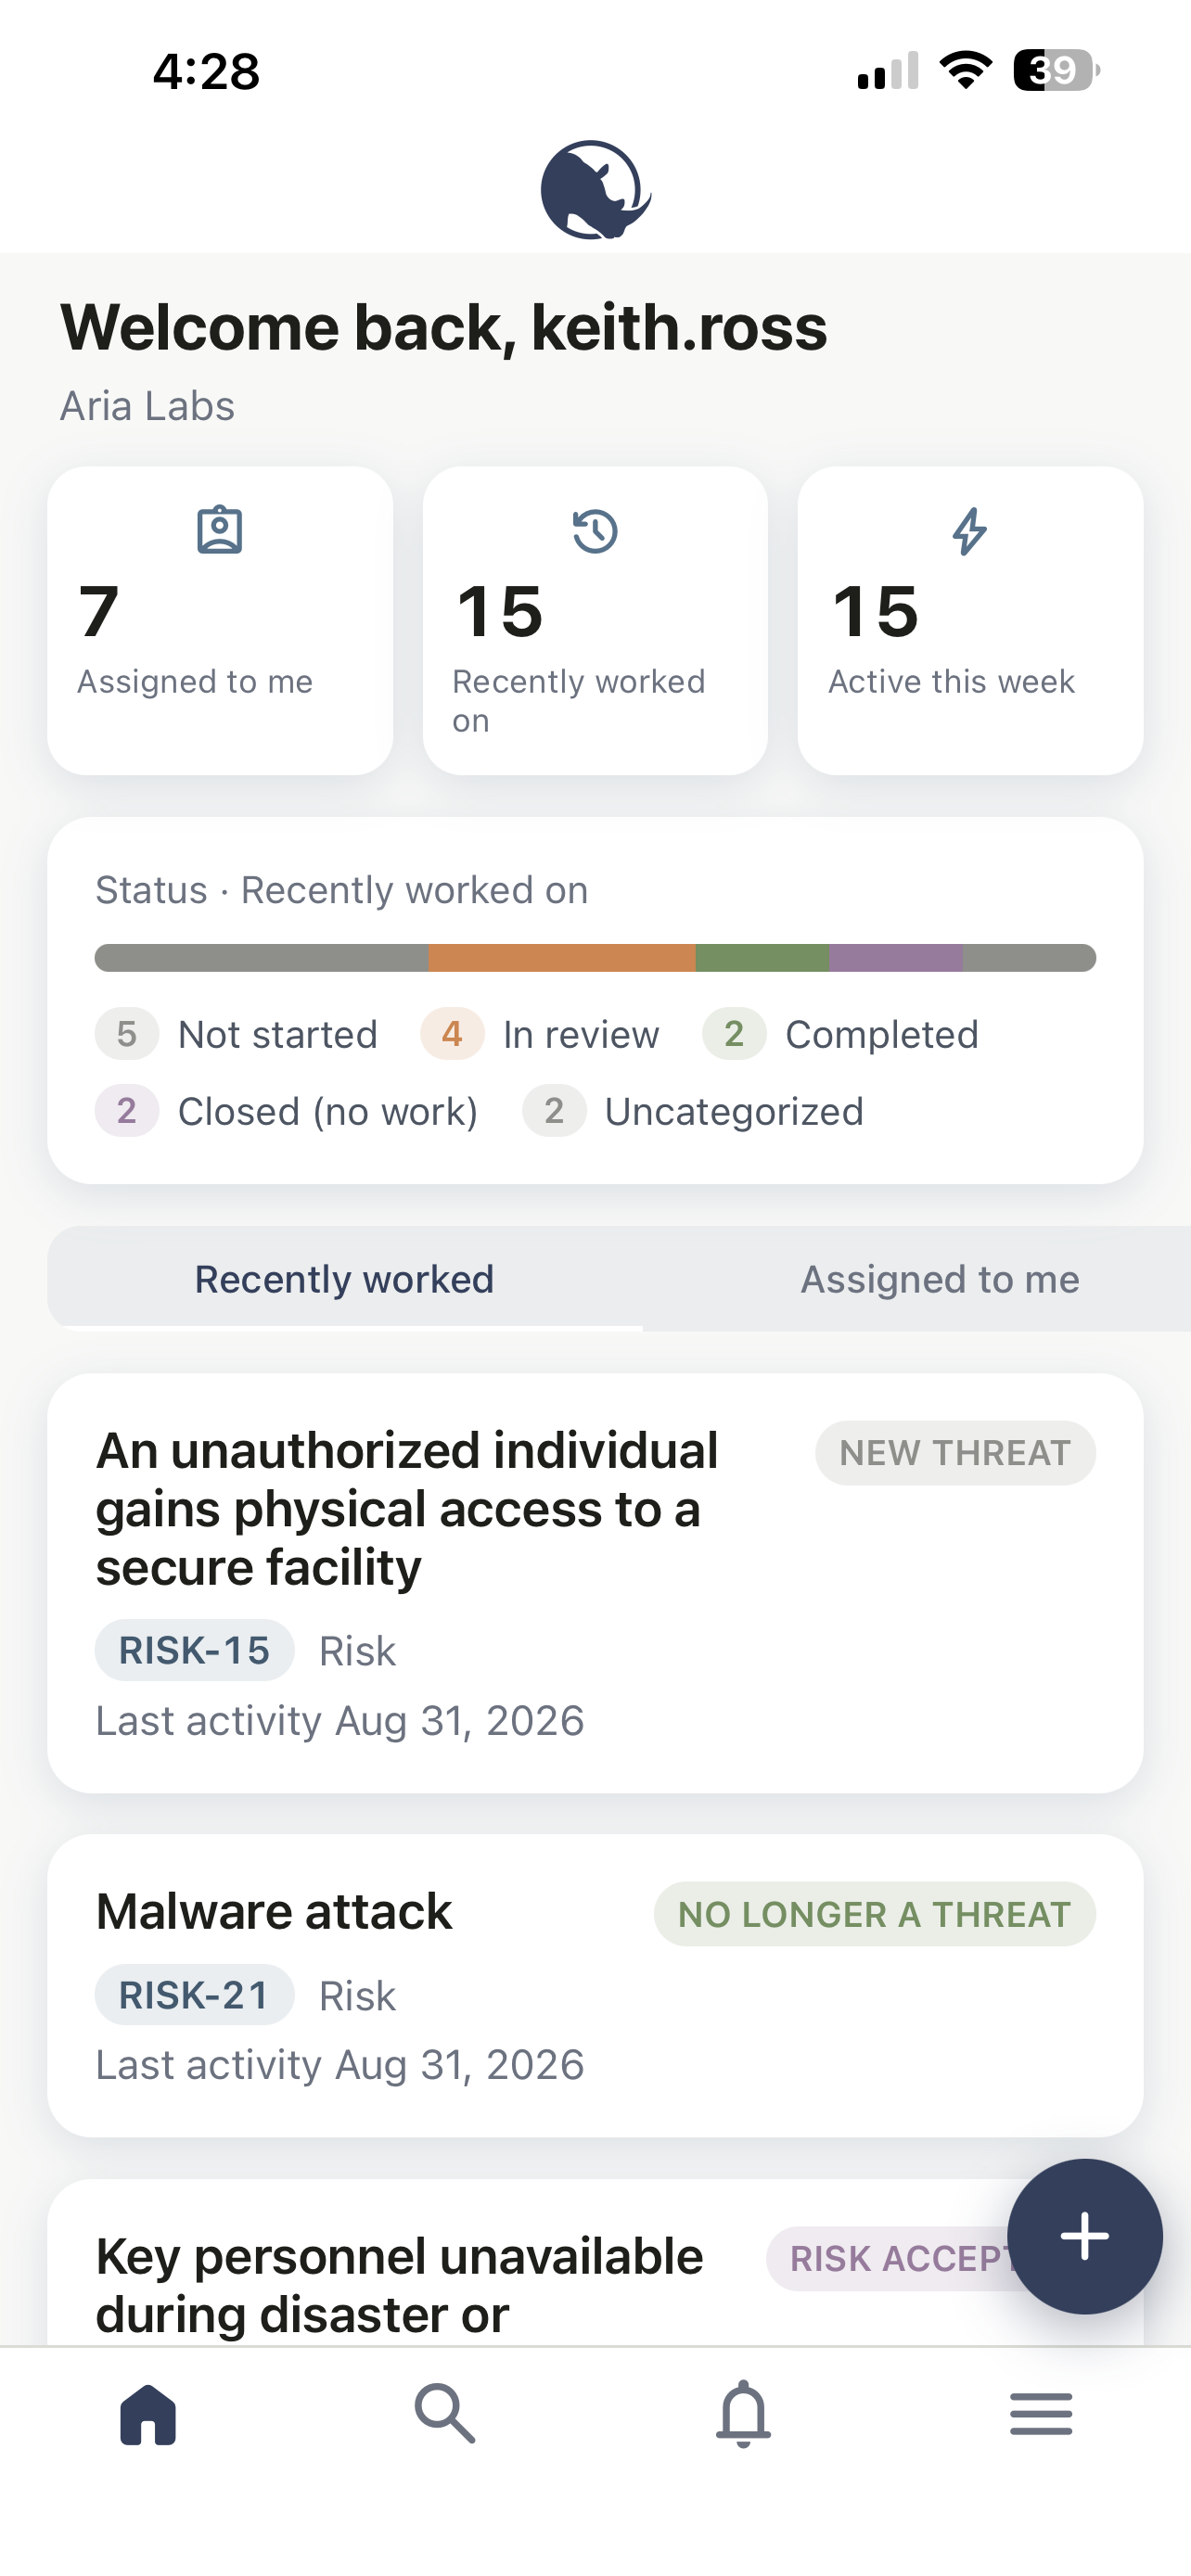
Compliance work does not wait for a desk.
domainGRC ships native applications for iOS and Android. Authorized users sign in to the same domain, see the same records, and work under the same permissions as they do on the web.
- Browse, edit, and file issues of any type, from incidents to service requests
- Capture evidence with the device camera and attach it straight to a record
- Offline-first: anything captured without a signal is queued and syncs when you reconnect
- Push notifications when a record needs your attention
Accounts are created by your organization for its own authorized users, so there is no public sign up and nothing new to administer. The apps are a second way into the program you already run, not a separate system to keep in step.
What you can do on day one.
One system, one set of records, and an internal audit capability for reviewing your program before your assessor does.
- See the whole program at a glance: audit status, upcoming activities, overdue tasks, risk distribution, and corrective action progress in one configurable dashboard.
- Work every framework control as a structured record. SOC 2 TSC criteria, ISO 27001 Annex A controls, and HIPAA safeguards are imported at onboarding.
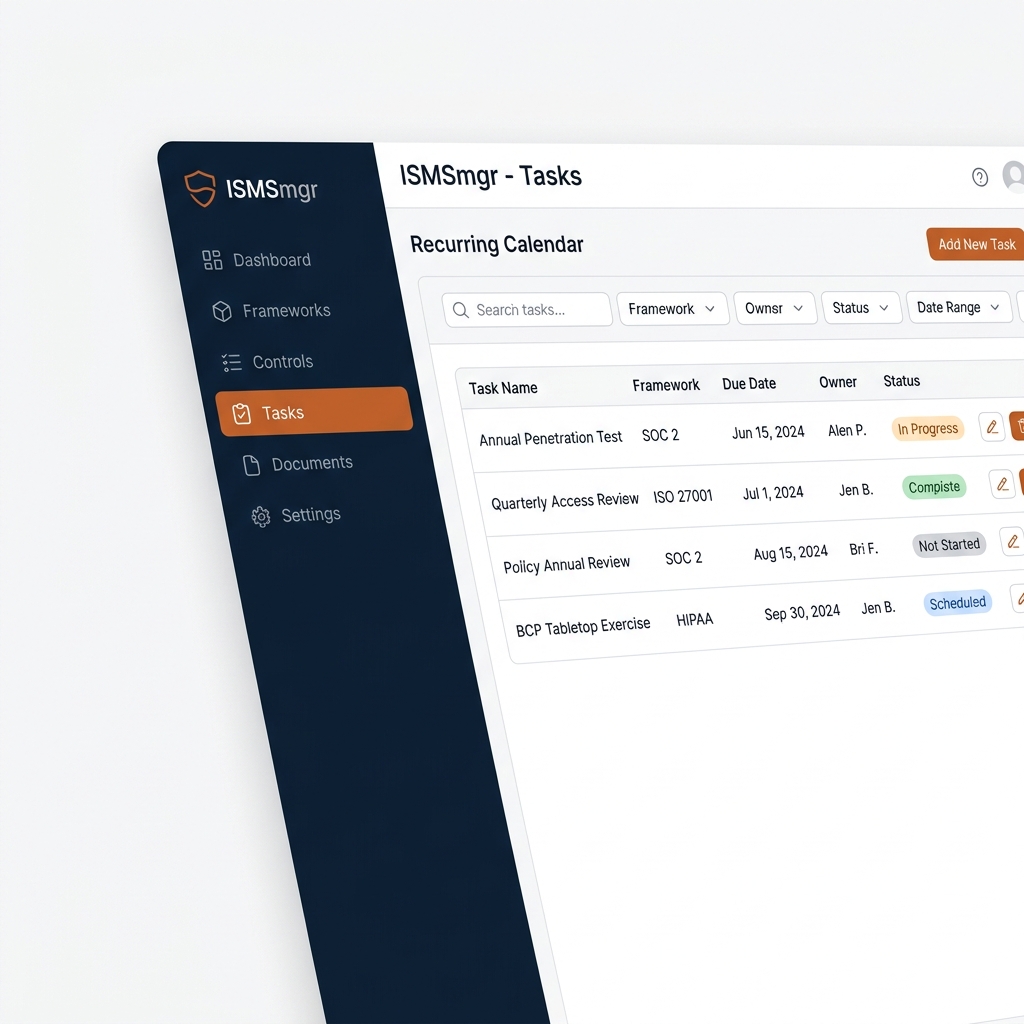
- Run a compliance calendar year-round, pre-loaded with the recurring activities a standard SOC 2 program expects: vulnerability scanning, pen testing, policy review.
- Keep a structured risk register: log every known threat, assign a rating, link it to corrective actions, and track remediation to closure.
- Manage corrective and preventive actions in one place, each linked to the risks, controls, and assets it touches.
- Run the policy lifecycle and reference the current version of every policy, standard, and procedure your program needs.
- Hold a complete compliance inventory: users, software, services, IT assets, information assets, and attachments.
- Assess third-party risk in the same system, documenting each vendor’s profile and linking them to the software assets they touch.
- Run onboarding, offboarding, and access requests through a built-in service desk, so the evidence for those controls captures itself in the normal course of work.
- Record changes and security incidents where the rest of the program lives, instead of in a separate tool nobody links back.
- Load your assessor’s Information Request List, assign evidence, and track each item through to acceptance.
- Store every artifact once, with version history and reuse across frameworks.
- Build the report you need in seconds: filter, sort, group, and configure any view, then save and export it.
Every framework your program requires. No per-framework fees.
domainGRC ships with framework controls for the certifications your business needs. Public frameworks like SOC 2 and NIST are ready on day one. For frameworks with proprietary specs (HITRUST, the ISO suite, and others), bring your purchased license and we load the controls in for you. Add additional frameworks and we map the overlapping controls automatically, so you’re not building from scratch. Capture evidence once and reuse it across multiple controls and frameworks.
Beyond the named frameworks, the platform is designed to be extensible. We’ve supported customers running ISO 9001, 14001, and 45001, NIST SP, NAID AAA, e-Stewards, R2v3, and RiOS programs, alongside the headline security frameworks. If your auditor accepts a framework, domainGRC can support it.
Risk management, corrective actions, third-party risk management, and internal audit capabilities are included in every plan. We don’t gatekeep the features you actually need to pass a real audit. And we don’t believe in nickel-and-diming you for streamlining your compliance program.